
Sonatype launches Nexus Repository Pro+ for AI screening
Tue, 27th Oct 2026 (Today)
Sonatype has launched Nexus Repository Pro+.
The product is designed to screen software components and AI artefacts before they enter development workflows.
The launch reflects a wider shift in how companies manage software supply chain risk, as developers and AI agents pull in dependencies with less manual review. The new product embeds malware detection and policy enforcement inside the repository, so checks happen when a package, AI model or Model Context Protocol server is requested, rather than later in the build pipeline.
The system can automatically block or quarantine components that are malicious, vulnerable or in breach of internal policy before they reach developers, AI agents or build systems. It applies those checks to open source packages, containers, AI models and MCP servers.
Sonatype linked the launch to new research on changing enterprise dependency patterns, particularly around AI-related artefacts and newer programming ecosystems. The findings suggest repositories are becoming a more important control point as enterprises broaden the range of external components they consume.
Adoption trends
The research found strong growth in enterprise use of Hugging Face, Go and Rust-related artefacts across the populations measured by Sonatype Research Labs.
Hugging Face appeared in nearly 6% of the measured Nexus Repository population, with nearly 4.7 times as many organisations adopting it in the second quarter of 2026 as in the same quarter a year earlier. Financial services and government accounted for nearly half of the observed adopters.
In a separate measured population, nearly 7% of Hugging Face requests were blocked or rejected by policy. That compared with just over 3.5% for Go and 1% for Cargo, Rust's package manager.
The reasons for blocking AI model requests went beyond conventional security screening. Of blocked Hugging Face models, 55% were rejected because of acceptability concerns, while 18% were rejected for security reasons, suggesting governance questions that traditional open source policies do not fully address.
Elsewhere, enterprise Rust adoption reached nearly 4.9 times its level in the second quarter of 2025, while new Go module creation rose 83% year on year in the first half of 2026. Go was already established across a meaningful share of measured enterprise repositories, while Cargo was expanding rapidly from a smaller base.
Point of entry
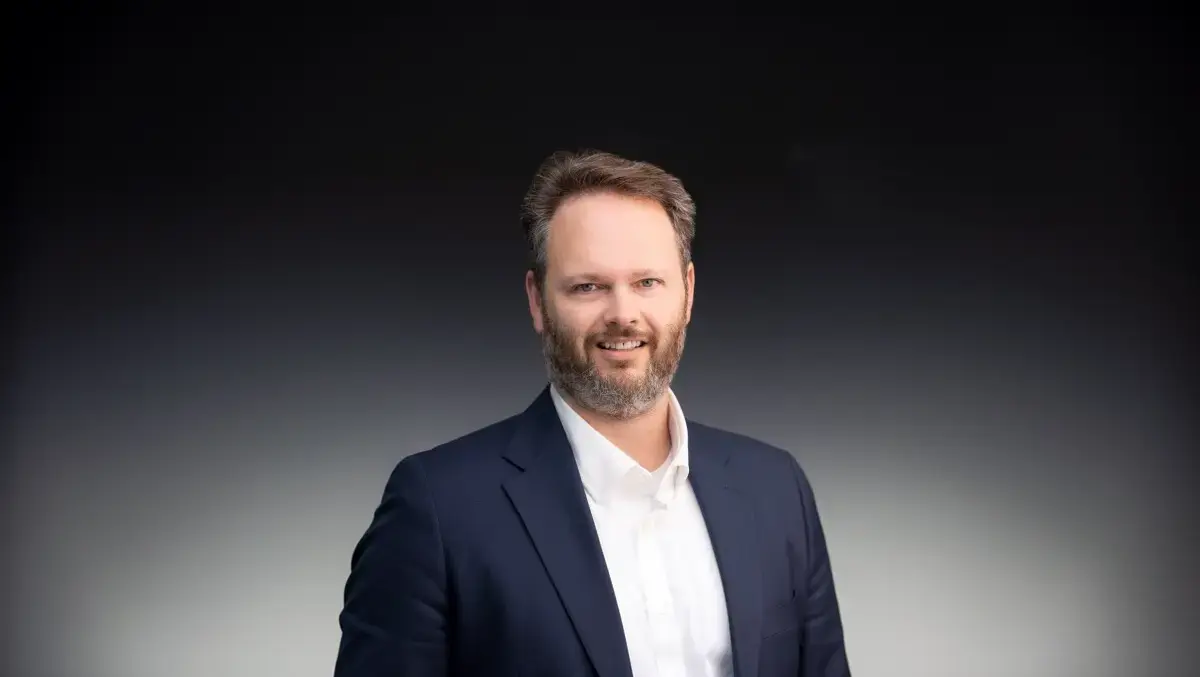
Brian Fox outlined the company's argument for shifting enforcement earlier in the software development process.
"When we built Nexus, the goal was to give developers a trusted foundation for using open source at enterprise scale," said Brian Fox, Co-Founder and CTO, Sonatype. "AI changed the equation. Developers and agents are pulling dependencies into builds faster than traditional review processes can manage, and attackers know it. Nexus Repository Pro+ puts the trust decision where it belongs - before a dependency reaches the build, not after it creates downstream rework or release risk. That's how you keep moving faster without giving up control over what you ship."
That approach contrasts with tools that identify issues after code and components have moved further into development and release pipelines. Late detection can leave teams dealing with failed builds, urgent upgrades and release delays.
Sonatype said its screening draws on threat intelligence informed by its stewardship of Maven Central and by its identification of more than 1.9 million malicious component versions. It added that organisations can apply internal security, legal, architectural and component-age policies at intake, using a catalogue of more than 333 million components.
The product is also intended to reduce remediation work later in the process by identifying safer upgrade paths and validating proposed changes against existing build and test processes.
Control and governance
The push for tighter controls comes as regulators place greater emphasis on software supply chain security. Sonatype pointed to reporting obligations under the EU Cyber Resilience Act for manufacturers of products in scope, arguing that preventing known-bad components from entering software supply chains carries more weight as compliance demands rise.
A customer comment issued with the launch underlined how governance is becoming more prominent as AI tools are woven into engineering work.
"At TD Bank, we are focused on ensuring our software supply chain is resilient and secure, while maintaining the rigor, reliability, and confidence our clients expect," said Mark Paulsen, Head of the Open Source Program Office, TD Bank. "As AI becomes more embedded in software development and the open source ecosystem, how we set controls and how we govern will be increasingly important in the years ahead. We need to give our development teams the open source guardrails needed to innovate and ship software with confidence in a way that doesn't slow down innovation or take our engineers out of the flow."