

Logicalis & Pentera launch continuous security validation
Fri, 25th Sep 2026 (Today)
Logicalis has partnered with Pentera to offer continuous security validation to organisations in Ireland, expanding its cyber security services in the market.
The partnership focuses on tools that let customers simulate real-world attack techniques in production environments, test security controls, and prioritise remediation based on confirmed exposure rather than assumed risk.
Security teams are under pressure to monitor a broader mix of cloud, hybrid, and AI-enabled systems as attacks become more varied and harder to detect. That shift is making periodic penetration testing less effective on its own, particularly where infrastructure and user identities change frequently.
Continuous validation is intended to give organisations an ongoing view of weaknesses as systems evolve, rather than relying on annual checks or one-off assessments tied to specific projects. It can help security teams identify which issues create an exploitable path for attackers and which can wait.
Research commissioned by Logicalis found that 71% of CIOs in Ireland, the UK, and the Channel Islands reported a cyber security incident in the previous 12 months. The same study found that 63% believed staff lacked the skills needed to use AI responsibly, raising potential compliance and reputational risks.
The survey was conducted by Vanson Bourne among 1,000 global CIOs, including 100 respondents in Ireland, the UK, and the Channel Islands. Respondents worked in organisations with 250 to 5,000 employees, and almost all were involved in decisions on AI implementation.
Testing shift
The deal reflects a broader move by service providers and security vendors towards more frequent testing of live environments. As organisations add cloud services, remote access tools, and AI systems, the number of potential entry points for attackers tends to increase, while fixed annual tests may capture only a snapshot.
The service is expected to be relevant to regulated sectors including financial services, manufacturing, and utilities, where operators face scrutiny over resilience and control effectiveness. For those businesses, proof that controls work in practice can matter as much as the existence of formal policies.
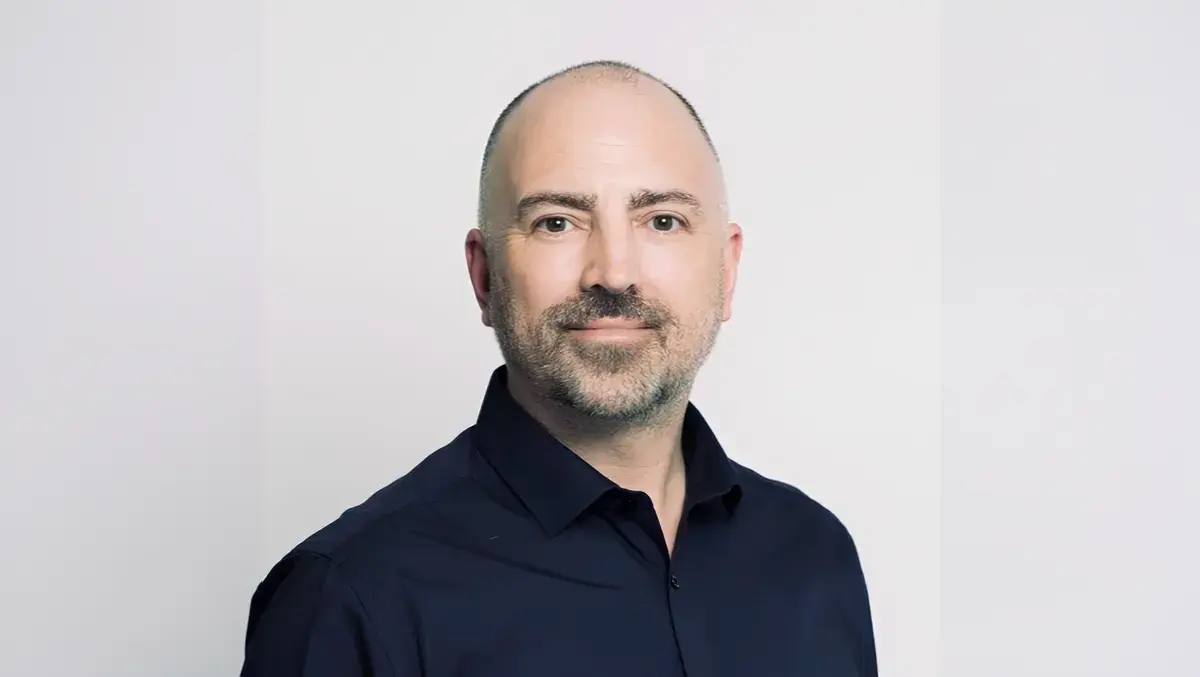
Mike Fry, Infrastructure, Data & Security Solutions Director at Logicalis UK&I, outlined the rationale for the move.
"The threat landscape facing organisations today is evolving faster and becoming more sophisticated than ever before. Relying solely on annual penetration tests or ad-hoc testing around new projects no longer provides the level of assurance businesses need. We're seeing a clear upward shift towards an always-on approach to security validation, particularly across highly regulated industries such as financial services, manufacturing and utilities, where organisations can continuously understand their exposure to real-world attacks as their environments change," said Fry.
Partner roles
Logicalis provides technology and managed services across cloud, connectivity, collaboration, and security. The group operates in 30 territories and reports annualised revenue of USD $1.63 billion. Parent company Datatec reports revenue of more than USD $3.6 billion.
Pentera focuses on automated security validation and has operations across North America, Europe, and Asia-Pacific. Its platform is designed to help organisations emulate attacks safely, identify attack paths, and measure whether existing controls can stop them.
Sivan Harel, SVP of Sales, EMEA, at Pentera, said the partnership combines the two companies' strengths in managed environments and security testing.
"Logicalis' ability to design, manage and secure complex digital environments aligns strongly with Pentera's mission to make cyber risk visible, actionable and remediated. Together, we are enabling customers to continuously validate security controls and efficiently address the security exposures that matter most," said Harel.
The combined offer is intended to give customers continuous insight into exploitable risk, evidence to support remediation priorities, and a clearer view of whether security spending is addressing the right threats.